Hoard less, protect more:
Securing data in the AI age
Millions of cyberattacks exploiting two critical vulnerabilities in a widely used programming language for websites and internet applications forced governments, institutions, businesses and other organizations temporarily offline last week.
The two gaps, collectively known as PHP2Shell, allowed attackers to execute malicious code on exposed web servers, potentially stealing sensitive data or disrupting services. Artificial intelligence helped security researchers discover the vulnerabilities, which dated back to memory code written by humans in 2012. Cloudflare, an American web services company, recorded millions of attempts to exploit gaps once they were publicized. Organizations worldwide had to temporarily halt many web services as a precaution while security updates were installed.
In addition to cyber damage like this, which was carried out by autonomous AI agents acting on their own, we see various other cyberattacks, including by criminals, hacking different sources – all of them illegal.
The most precious commodity
Data has arguably become the most valuable commodity in the world. Items of worth always attract desire, either to steal to gain advantage, or to destroy if they relate to an adversary. There are also combinations of both.
The entire digital and AI domain is new; technicians and scientists have not yet learned to protect them properly. If you have valuable assets, one of the most important issues is their protection from wrongful exploitation.
Technological development is crucial if this realm is to enhance general productivity.
We should use central registers in a very limited way only, while being cautious which data we include.
Prince Michael of Liechtenstein
One element of data protection is to make data difficult to find, part of which involves storing it at multiple locations to reduce the risk of losing everything. Unfortunately, Western societies adore centralization; more and more central registers of citizen data are being established, to which increasing numbers of people have access.
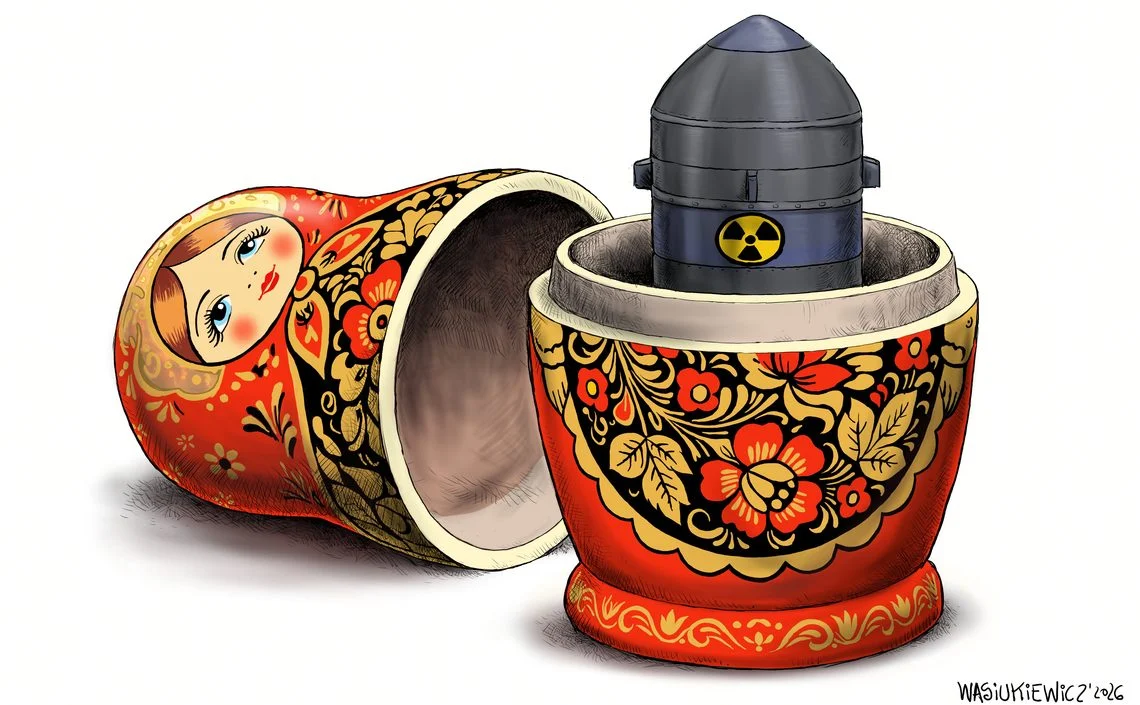
In Europe, GDPR should help to limit collection and storage of too much data. However, both the European Union and nearly all states have secured exemptions to regulations – GDPR is not applied when nations collect data under special legislation.
As governments centralize data for different reasons, there is a major element of control involved. The general pretext is to support the prosecution of criminal activities. But this has its downsides.
Irresistible target for adversaries, criminals and governments alike
This collection of data is a welcome target for criminal organizations and foreign powers. Voyeurism is encouraged under two pretexts: whistleblowing and the “legitimate” interest of journalists. Central registers are even planned on the EU level for bank accounts, including amounts. Additionally, national data collection does not preclude misuse by individual governments to control their own citizens. This is a critical issue posing an illiberal risk of overstepping and limiting citizens’ rights and freedoms.
In the political competition between power blocs, stealing, paralyzing or destroying data is becoming very important. In this area, state actors collaborate with organized crime. Involving criminal organizations gives foreign actors a wonderful opportunity for deniability.
In the context of leadership in biological and medical development, medical data is also becoming very important. While it is difficult to blackmail an individual with medical data, such data is crucial for legitimate development of drugbots and treatments, but also for malicious biological weapons.
Better safe than sorry
Certainly, we need to use digital possibilities and AI to handle data, but we have to be more careful. We should use central registers in a very limited way only, while being cautious which data we include.
Financial data is extremely vulnerable because it is as important for criminal and foreign powers as it is for tax collection purposes. Tax offices already have other sufficient possibilities to access the information. This is also the case for police and prosecutors.
In Europe, much has been done to regulate the digital world and AI. Yet it is necessary not only to emphasize regulation, but to focus on security and citizens’ right to privacy.
If Western governments would be more careful to preserve the legitimate privacy of their populations, it would mark a major step toward data security.
The priority is security, not a bureaucratic collection of data in central registers.
Our Partners